Published: September 24, 2026
Last Updated: September 24, 2026
Quick Answer: A business password manager gives employees one secure place for work credentials. Administrators control access, sharing, security policies and account changes. Configure permissions correctly and password reuse drops. Onboarding and offboarding get easier too.
Businesses face a different problem than individual users. Employees share accounts. Contractors need temporary access. When someone changes roles or leaves, an administrator has to pull that access back.
Shared vaults, permissions, user management and reporting cover those needs. Controls vary by provider, though. Storing passwords is the baseline. Look at how much control you get over who reaches which credentials. And when.
The National Cyber Security Centre says organisations should consider password managers. Less password overload, better password quality. It flags risks too. Password managers carry some of their own, so encryption, access controls, recovery and usability all matter when you pick one. NCSC’s password manager buyers guide backs this up.
A business password manager is software that stores work credentials in protected vaults while providing administrative controls for assigning, monitoring and removing access across a team.
What to Look for in a Business Password Manager
| Business need |
What to look for |
| Shared credentials |
Shared vaults or collections with role-based permissions |
| Employee access |
Individual and group-level access controls |
| Password security |
Password generation, reuse detection and security policies |
| Team administration |
User provisioning, suspension and offboarding controls |
| Security oversight |
Activity logs, reports and password-health information |
| Larger organisations |
SSO, directory integration and SCIM provisioning |
| Temporary access |
Time-limited sharing and controlled external access |
Why do businesses need password management?
Employees juggle a lot of accounts. Shared credentials add access and offboarding problems on top. A central system makes unique passwords easier to use, and nobody has to remember them all. Decision-makers weighing a business tool can start with how a password manager works. It shows whether the tool fits your team’s login, sharing and access-control needs.
The NCSC says password managers cut the burden of managing many passwords. Organisations also use stronger, unique credentials more consistently. Still, check a few things before deployment. Access controls, recovery, encryption, cloud-security considerations and usability.
The business case becomes clearer when several people need the same account. A password stored in a spreadsheet, document, email or chat message is difficult to control after it has been copied. A dedicated business system can instead assign access through users, groups or shared vaults.
There is also a practical distinction between storing passwords and managing access to passwords. A consumer password manager may solve the first problem, while a business product may add central administration, reporting, provisioning and team permissions.
A password manager does not remove every security risk. The NCSC specifically notes that password managers can become attractive targets because successful access could expose many stored credentials. The product therefore needs strong protection around the vault itself, and employees still need secure authentication practices.
For businesses, the strongest setup is usually the one employees can use consistently while administrators retain appropriate control.
How business password managers control access
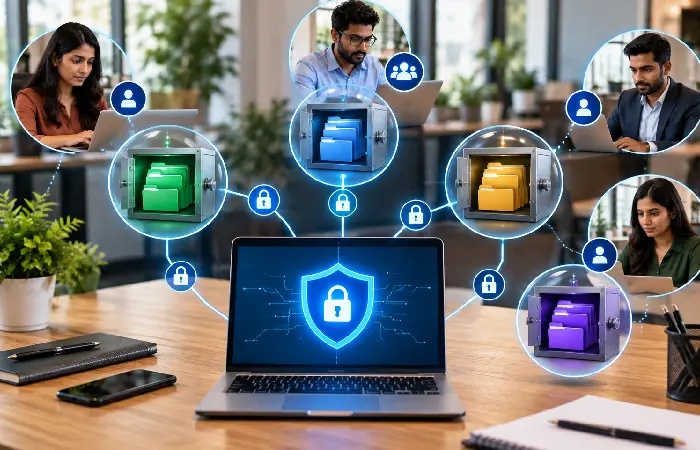
A business password manager controls access by connecting credentials to users, groups, vaults and permissions. Instead of giving every employee the same collection of passwords, administrators can limit access to the accounts required for each person’s role.
For example, a marketing employee may need access to advertising and social media accounts, while an accountant may need access to financial platforms. Those employees do not necessarily need access to each other’s credentials.
Use shared vaults and groups
Shared vaults let teams work with common credentials without sending passwords through ordinary communication channels. Administrators can organise access around departments, projects or specific business functions.
The exact permission model depends on the product. 1Password Business, for example, documents vault-level permissions that can control actions such as creating, editing, exporting and sharing items.
Give people access to the credentials they need. Nothing more. Skip the big shared collections that mix in unrelated accounts.
Apply least-privilege access
Least privilege means a person gets only the access their role requires. Fewer credentials exposed. That holds if an employee account is compromised, and it holds if someone’s role changes.
1Password’s business guidance specifically recommends keeping permissions to the minimum needed and using focused vaults rather than broad, general-purpose vaults. 1Password’s business security guidance documents this approach.
This is one area where a business password manager is more useful than a shared spreadsheet. The goal is not simply to hide the spreadsheet. It is to make access itself manageable.
Control onboarding and offboarding
New hires and leavers are one more reason businesses need centralised credential management. Someone joins, and access can be assigned according to their role. Someone leaves? Their account can be suspended or removed. Shared credentials can be reviewed too.
This does not automatically mean every password the employee previously saw becomes safe again. If an employee knew a shared password, that credential may still need to be changed after access is revoked.
That distinction matters. Revoking account access and changing a shared credential are separate actions.
Secure password sharing for teams
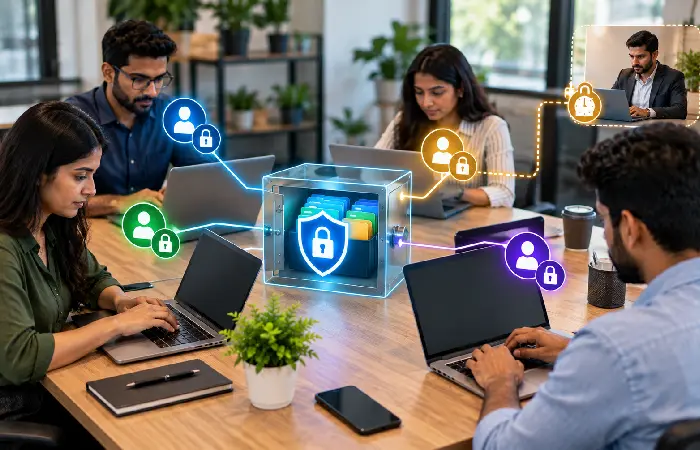
Secure password sharing lets employees use common business credentials. No email. No chat messages. No shared documents. The safest approach comes down to control over who receives access, plus how long it stays available.
Business password managers commonly use shared vaults, collections or individual item-sharing controls. Some also provide temporary access for contractors or external partners.
For example, 1Password Business lets administrators manage item-sharing settings. Max link lifespan, default expiration period. Both are adjustable. Options include one hour, one day, seven days, 14 days and 30 days. Which one? Depends on how sensitive the credential is and what the sharing request is for.
Give access instead of sending passwords
Suppose three employees need the login for a business service. Sending the password through email creates a copy that may remain in inboxes, message history or other systems.
A shared vault can instead provide controlled access to the credential. If one employee leaves, administrators can remove that person’s access without needing to find every message where the password was sent.
The approach works best when the shared vault is narrowly defined. A vault containing every company credential creates a much larger access problem than a vault containing only the credentials required by one team.
Use temporary access for contractors
Contractors, agencies and external partners often need access for a limited period. If the selected product supports external-sharing restrictions or link expiration, configure those controls before access is granted and review access again when the engagement ends.
Do not assume temporary sharing means the underlying credential is permanently protected. If the recipient can view or copy the password, the business may still need to change that credential after the engagement ends.
Avoid shared master accounts where individual accounts exist
A password manager should not become a reason to keep using one shared account when the underlying service supports individual user accounts.
Individual accounts provide clearer accountability and make access removal easier. Shared credentials remain useful for services that genuinely require one account, but they should be treated as a specific business requirement rather than the default for every application.
Admin, audit and security features to look for
A business password manager should give administrators enough control to manage users, permissions and security without exposing everyone’s passwords. The right feature set depends on company size and the systems employees use.
| Feature |
What it should provide |
| Admin console |
Central management of users, groups and security policies |
| Access controls |
Role- or group-based access to specific credentials |
| Activity logs |
Records of relevant account, sharing or access events |
| Password health |
Visibility into weak, reused or exposed credentials where supported |
| MFA support |
Additional authentication for the password manager account |
| User provisioning |
Faster creation and removal of employee accounts |
| SSO |
Centralised authentication through a supported identity provider |
| SCIM |
Automated user and group provisioning where supported |
| Recovery controls |
A documented way to recover access without bypassing security |
| External sharing controls |
Restrictions and expiration for sharing outside the organisation |
The NCSC advises system owners to consider encryption at rest, access to credentials, account recovery and the security implications of cloud-based password managers. Its password manager buyer guidance provides the framework for assessing these areas.
Audit logs and password health
Audit features help administrators understand how the system is being used. Depending on the product, reports may cover login activity, sharing events, password reuse, password strength or MFA adoption.
Depending on the product and subscription tier, organisation-level reporting may cover password strength, password reuse, exposed credentials, MFA adoption, logins, password changes and sharing events. Confirm the exact reports, retention period and export options during product evaluation.
Use these reports to manage the system. They don’t prove the organisation is secure. A clean dashboard still can’t make up for excessive permissions. Weak account recovery, poor employee adoption, same story.
SSO and SCIM
Larger teams may get real value from connecting an identity provider. SSO can centralise authentication. SCIM can automate provisioning for users and groups, provided both the identity provider and the password manager support it.
These features become more useful as employee numbers and application counts grow. A small business with a few employees may not need the same provisioning architecture as a larger organisation.
Recovery matters as much as access
Before deploying a password manager, decide what happens if an administrator loses access or an employee leaves unexpectedly.
Document the recovery process first. Before the organisation depends on the vault. 1Password’s business guidance, for example, recommends planning for account recovery. It also says important shared information should stay accessible when an owner or administrator becomes unavailable.
How to choose a password manager for your business
Pick a password manager based on your team’s access model. Required integrations, recovery needs, and administrative controls. Don’t choose one just because the interface looks familiar or the feature list runs long.
Use this process:
1. Map the credentials you need to manage.
List the types of accounts employees use, including shared services, individual accounts, administrator accounts and credentials used by contractors.
2. Define who needs access
Group employees by actual work requirements. This gives you a starting point for shared vaults and permissions.
3. Decide how employees will authenticate
Check support for MFA, SSO and your existing identity provider if those controls are required.
4. Check provisioning and offboarding
Determine how users are added, suspended and removed. For larger teams, check whether SCIM or directory integration is supported.
5. Review sharing controls
Look for granular permissions and controls for external or temporary sharing.
6. Check audit and reporting features
Confirm which activities administrators can review and whether reports meet your operational needs.
7. Test recovery before deployment
Write down what happens in three cases. An administrator loses access. An employee leaves. And when a critical credential has to be recovered, the steps should already be on paper.
8. Pilot the setup with a small group
Test the actual access structure before moving the entire company. Pay particular attention to shared vaults, permission boundaries and offboarding.
The most important selection criterion is fit with the organisation’s access model. A feature-rich product that employees bypass can leave the original password-sharing problem in place.
The NCSC makes a similar point in its organisational guidance: usability matters because employees who find a password manager difficult to use may continue relying on insecure workarounds.
When a business password manager may not be enough
A password manager is not a replacement for an identity and access management strategy.
Does the application support individual accounts and SSO? Use those controls where appropriate instead of relying on one shared password. Passkeys need their own look on systems that support them. Businesses should also evaluate whether passwordless authentication fits the use case. Passkeys are designed to resist common phishing attacks because the credential is bound to the legitimate site or service. Organisations still need to manage device access, recovery and account lifecycle controls.
A password manager doesn’t remove the need for MFA. Or endpoint security, software updates, phishing awareness and sensible account permissions.
Before sensitive company credentials go in, businesses should also understand whether password managers are safe. Especially when evaluating encryption, account recovery, MFA and vendor security practices.
Common mistakes when managing business passwords
The most common mistakes are usually related to access design rather than the vault itself.
Giving everyone access to every vault
Broad access is easier to configure, but it exposes more credentials than most employees need. Create smaller vaults or groups around actual business responsibilities.
Forgetting credentials after employee offboarding
Removing an employee from the password manager does not necessarily change credentials they previously knew. Review shared accounts and rotate sensitive passwords when access changes require it.
Using the password manager without MFA
The password manager itself protects many other credentials, so its primary account needs strong authentication. CISA recommends using multifactor authentication as part of account protection.
Treating audit reports as automatic security
A report nobody reviews is useless. Same if nobody acts on the findings. Decide who owns access reviews. Decide how often they happen. And what happens when a risky credential is identified?
Ignoring recovery planning
A company can create a security problem by designing access controls so tightly that nobody can recover critical business credentials. Establish recovery responsibilities before the vault becomes essential to daily operations.
Frequently asked questions
1. What is a password manager for business?
A password manager for business stores work credentials in protected vaults and adds controls for managing users, permissions and shared access. Business versions can also provide administration, reporting, provisioning and security-policy features.
2. Why should a business use a password manager?
Employees get unique passwords that are easier to use. Access to shared credentials stays under the business’s control. Less reliance on insecure password-sharing methods, too. Employee access changes get easier to manage.
3. Can employees share passwords securely with a business password manager?
Yes, when the product provides controlled sharing features. Businesses should use permissions, shared vaults and, where available, temporary or restricted sharing rather than sending credentials through ordinary email or chat.
4. Can a password manager help with employee offboarding?
Yes. A business password manager can make it easier to remove an employee’s access to managed credentials. However, shared passwords that the employee already knew may still need to be changed.
5. Should small businesses use a business password manager?
A small business can benefit when several employees need to manage work credentials or shared accounts. The required feature set may be smaller than what a large organisation needs, so the business should pay particular attention to usability, access controls and recovery.
6. Does a business password manager replace MFA?
No. A password manager and MFA address different parts of account security. MFA should also be enabled for the password manager account and other important services when supported.
7. What should I look for in a password manager for business?
Start with access controls, secure sharing, MFA, recovery, administration and audit features. Larger organisations should also check SSO, directory integration and SCIM support where those features fit their existing identity infrastructure.
Choose access control before extra features
A password manager for business is most useful when it gives employees an easy way to use secure credentials while keeping access under organisational control.
Start by mapping who needs which accounts. Then check sharing permissions, MFA, recovery, offboarding, reporting and integrations. If your business already uses SSO or an identity provider, make compatibility part of the selection process.
For the wider topic, see the password manager guide for the broader password-management framework.